









I'm a Senior DevOps / SRE / Platform Engineer at BukuWarung, where I build, secure, and scale high-throughput payment infrastructure serving 100K+ merchants across Indonesia. Four-plus years of end-to-end ownership: from Terraform modules and Aurora failover automation down to HSM key ceremonies and VAPT closure.
My default lens is security-first cloud engineering — if it touches money, it gets threat-modelled, encrypted in transit, least-privileged, and audited before it ships.
name:      Amsal Khan
role:      Senior DevOps Engineer @ BukuWarung (FinTech · Payments)
domain:    Payments, EDC/POS, QRIS, banking integrations
focus:     Cloud Security · Reliability Engineering · IaC · FinOps · AI Platform
cloud:     AWS (primary) · GCP
philosophy: "Automate the boring. Encrypt the rest. Alert on what matters."
ask_me_about:
  - Payment security (HSM, TMK injection, mTLS, X.509)
  - Zero-downtime Postgres/Aurora upgrades & partitioning
  - Terraform at scale, OIDC keyless CI/CD
- Cutting cloud bills without cutting reliability| Cloud spend eliminated across AWS + GCP via Graviton migrations, resource consolidation, log retention and BigQuery partitioning | Aurora failover recovery on the core payments platform, fully automated with zero manual intervention | Stateless Rust callback service meeting a 3s partner SLA on the QRIS payment path |
| Scale of the payment platforms I own reliability for, as on-call lead and RCA author | Driven from the SRE/Infra side — DR plans, runbooks and audit evidence across annual cycles | Internal AI agent platform on ECS/Fargate via Terraform, with LLM observability through Langfuse |
Security isn't a side quest for me — it's most of the job when the workload is regulated payments.
Cryptography & Key Management
- HSM-backed key management for payment terminals — master key custody and secure key injection, with mTLS between device and platform
- Device identity at fleet scale — per-device X.509 certificates over a managed PKI, replacing shared credentials
- Message-level integrity on partner payment flows — HMAC and RSA signature verification, plus PGP-encrypted file exchange with banking partners
Identity, Secrets & Access
- Keyless OIDC federation for CI/CD, so pipelines hold no long-lived cloud credentials
- Short-lived, audited database credentials issued on demand, and least-privilege secret distribution across environments
- SSO-enforced VPN fronting sensitive internal apps, plus custom IdP work to put per-credential network policy behind managed file transfer
Network Isolation & Assurance
- Private connectivity to banking partners and payment switchers over dedicated leased lines and IPSec tunnels in a hub-and-spoke topology
- Edge and WAF policy — TLS posture, origin protection and request-level access control as a self-service capability for engineers
- Owned VAPT cycles end to end, from finding triage through remediation to verification
Responsible Disclosure & Recognition
- 🏅 Reported a stored XSS vulnerability to Microsoft (MSRC) — 2018
- 🏅 Reported SQL injection (MySQLi) vulnerabilities to CPGRAMS, Government of India — 2018
- 🏅 Bug bounty awarded by PayPro Global — 2018
- 🏅 Star Performer of the Month among 100+ DevOps engineers at To The New — 2022
- 🔎 DevSecOps automation with Fortify WebInspect (DAST/SAST) for a leading insurer's compliance programme
- 🐍 Built an automated AWS security-audit tool in Python/boto3, cutting audit turnaround significantly
|
☁️ Cloud & Networking
|
🏗️ Infrastructure as Code
|
|
🔁 CI/CD & Containers
|
🔐 Security
|
|
🗄️ Data & Streaming
|
📊 Observability
|
|
💻 Languages
|
🤖 Automation & AI Platform
|






Contributor to the tooling I run in production — Langfuse, n8n and adjacent platform projects. Running something at scale tends to surface the rough edges worth fixing upstream.
Previously an Android custom ROM and kernel maintainer, shipping builds and device trees across several AOSP-based ROMs (Project-Xtended, Corvus-OS, NamelessAOSP). That work is retired now, but it's where I learned to read other people's systems code and debug things with no stack trace.
Selected personal projects:
| Project | Stack |
|---|---|
| AWS EKS Terraform Module | Terraform, EKS, VPC, S3, Docker — multi-AZ with autoscaling |
| Jenkins Multibranch CI/CD on EC2 | Jenkins, EC2, Docker, GitHub |
| Automatic Attendance Bot | Python, Selenium, Telegram API, Heroku CI/CD |
🔒 Most of my day-to-day engineering ships from a separate private work account. The first card aggregates that output — commit and PR volume only, no repository or project detail.


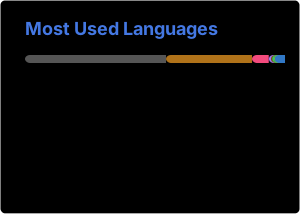

Cards generated by github-stats-extended via GitHub Actions — no external widget hosting to break.
⚡ Fun fact: I collect airports and timezones — travelling to new places is how I reset between incidents.
Let's build something reliable and secure.
md.amsalkhan@gmail.com ·
LinkedIn ·
Résumé